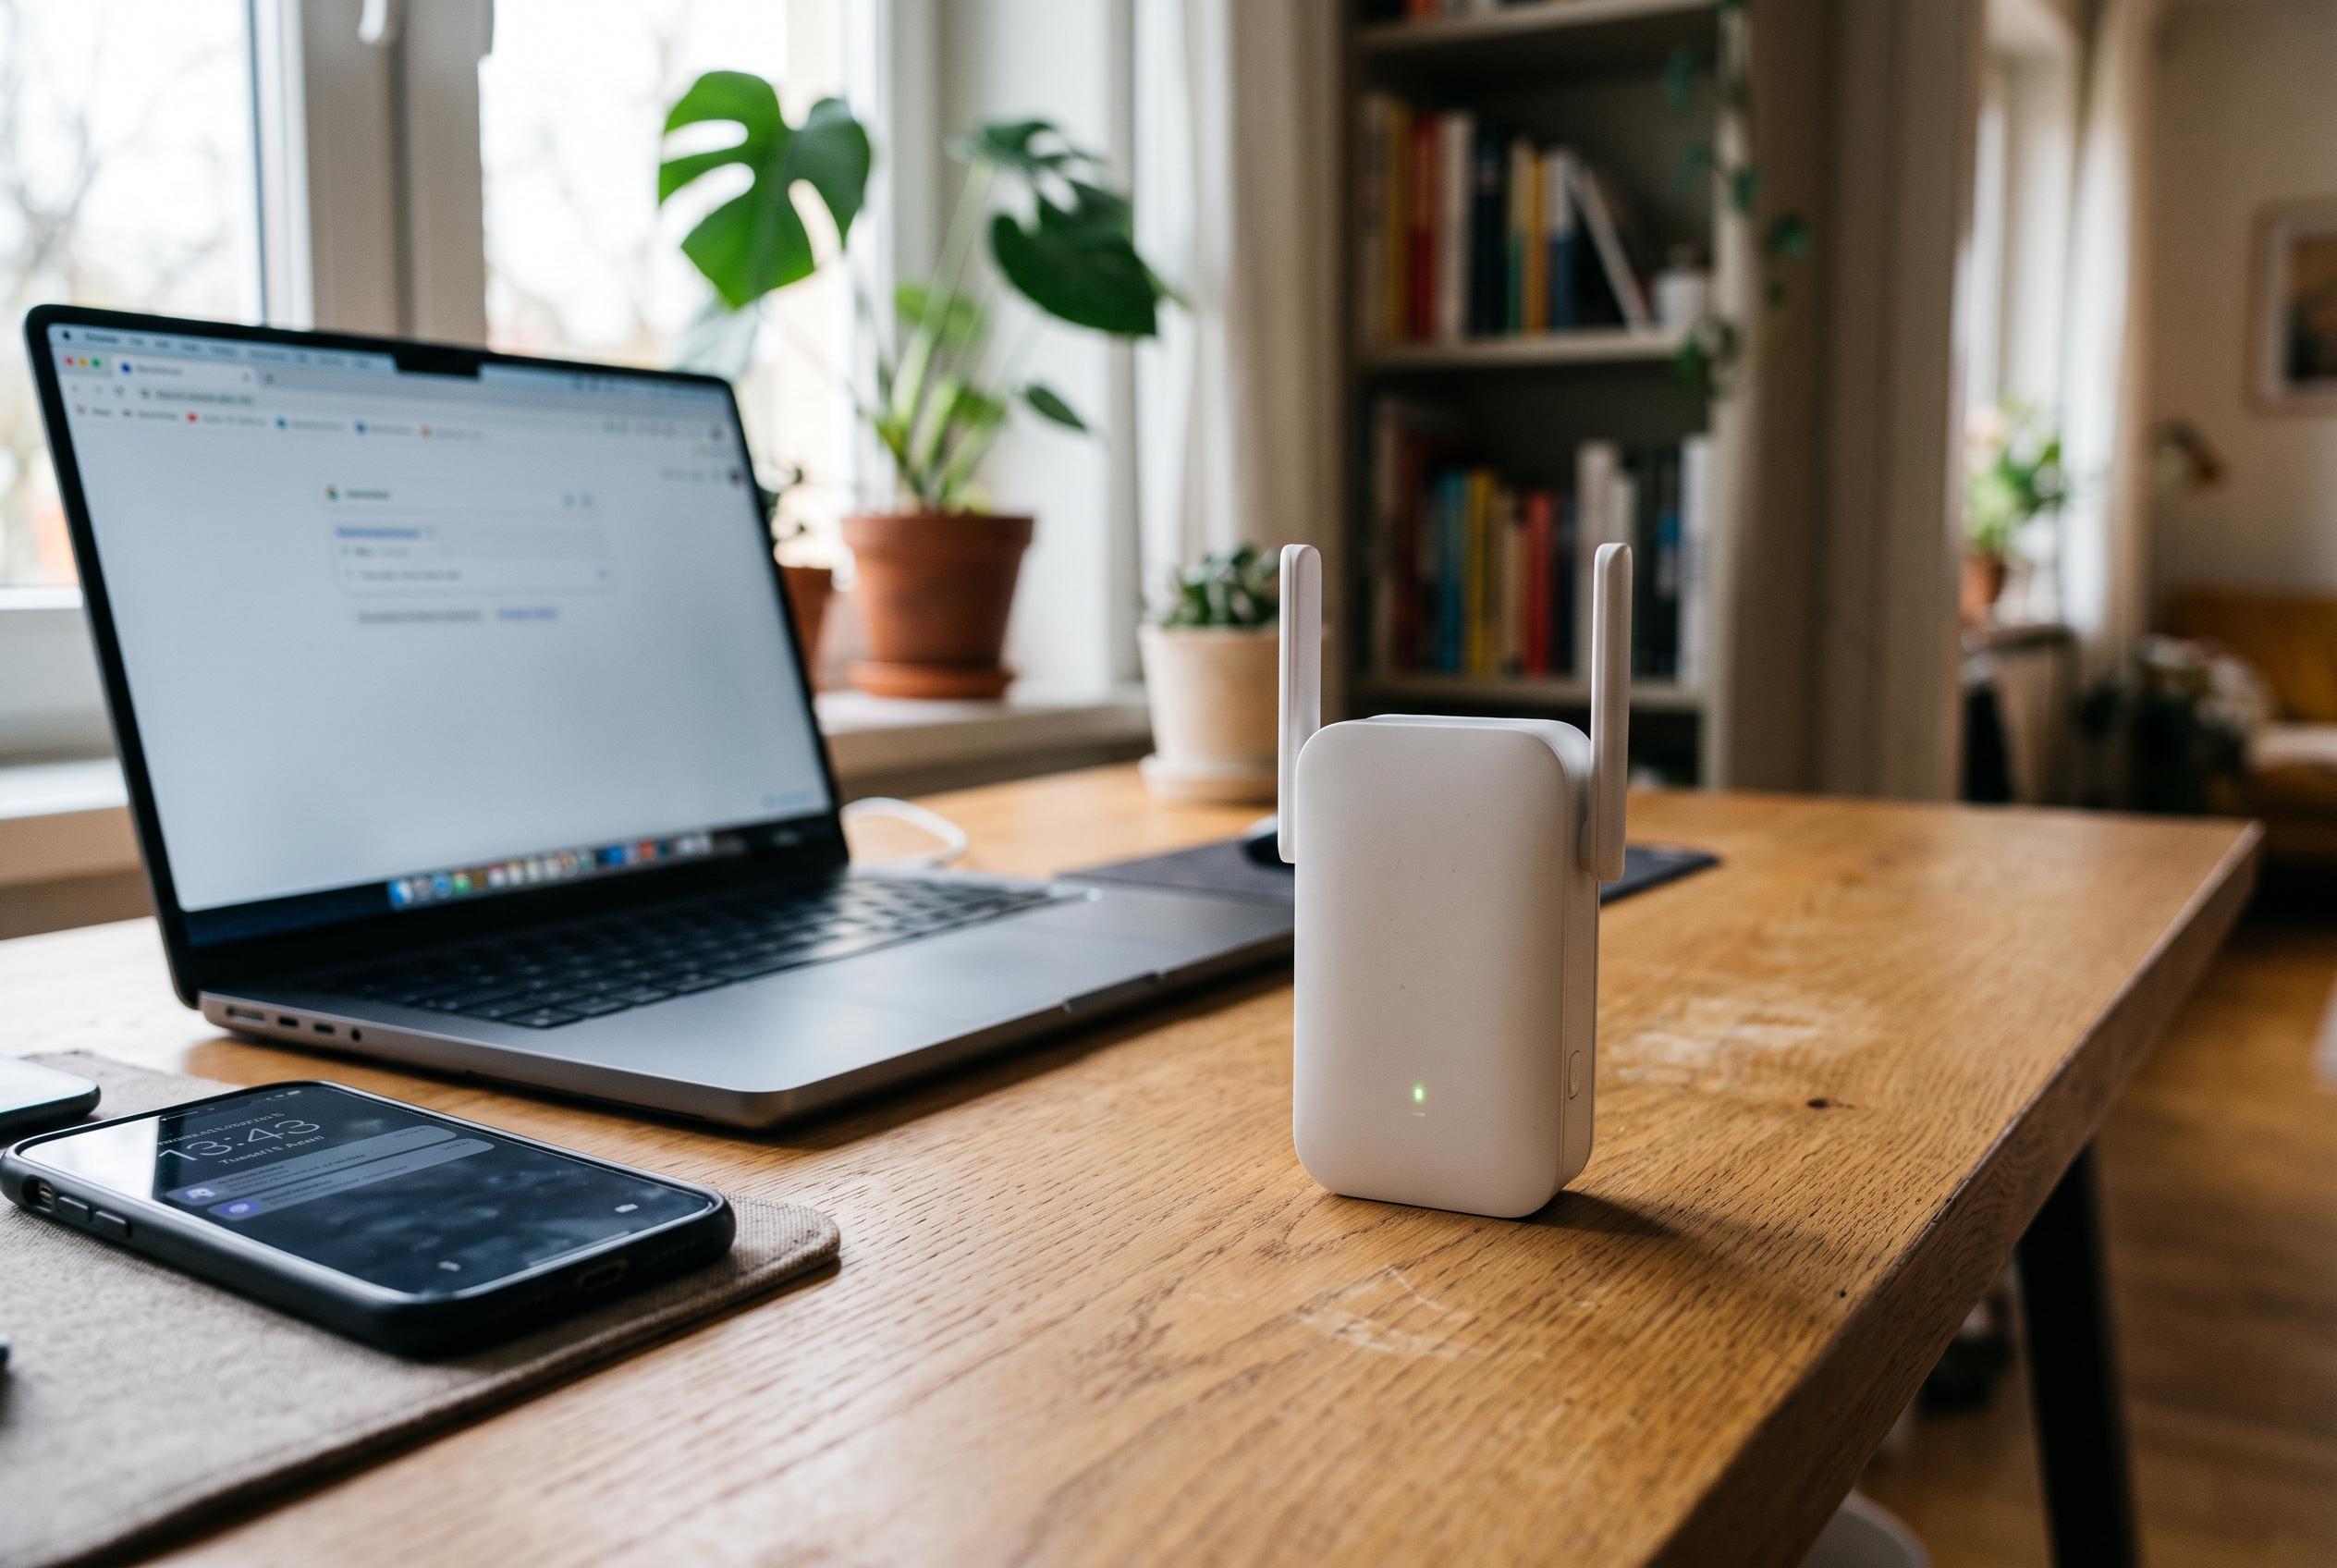

A £3 Wi-Fi extender sold through Temu was uncovered to contain concealed access features and vulnerabilities, raising concerns over cheap connected devices and their security implications.
A security researcher has shown that a £3 Wi-Fi extender bought through Temu carried hidden access features that ordinary users could not see or control, raising fresh questions about the safety of ultra-cheap connected hardware. According to TechRadar, Keiran Smith, a penetration-testing certified researcher, bought the six-antenna device after seeing it promoted in a targeted advert on the shopping app and then began examining its hardware and firmware.
Smith found that the extender used a MediaTek MT7620 processor and contained a concealed administrator account protected by a fixed password embedded in the software. That meant every device using the same firmware shared the same secret credentials, and changing the visible administrator password through the settings did not remove the hidden account. CyberNews reported that the account also allowed remote access without physical contact, making the flaw more serious than an ordinary default login.
The researcher also identified a remote login service that accepted the concealed credentials and said the password persisted in a way that could even survive attempts by an owner to change it. In comments quoted by TechRadar, Smith said this was worse than a standard default password because the user was never told about the account and could not meaningfully control it.
Beyond the hidden access, Smith found signs of a command injection weakness and weak software-update protection, which could open the door to tampered firmware. He said the problems did not prove deliberate wrongdoing by the manufacturer and could instead have come from factory testing processes left active before sale. Similar concerns have surfaced in other low-cost devices sold through digital marketplaces, with Consumer Reports warning earlier this year that some video doorbells on platforms including Temu shared serious security flaws.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.