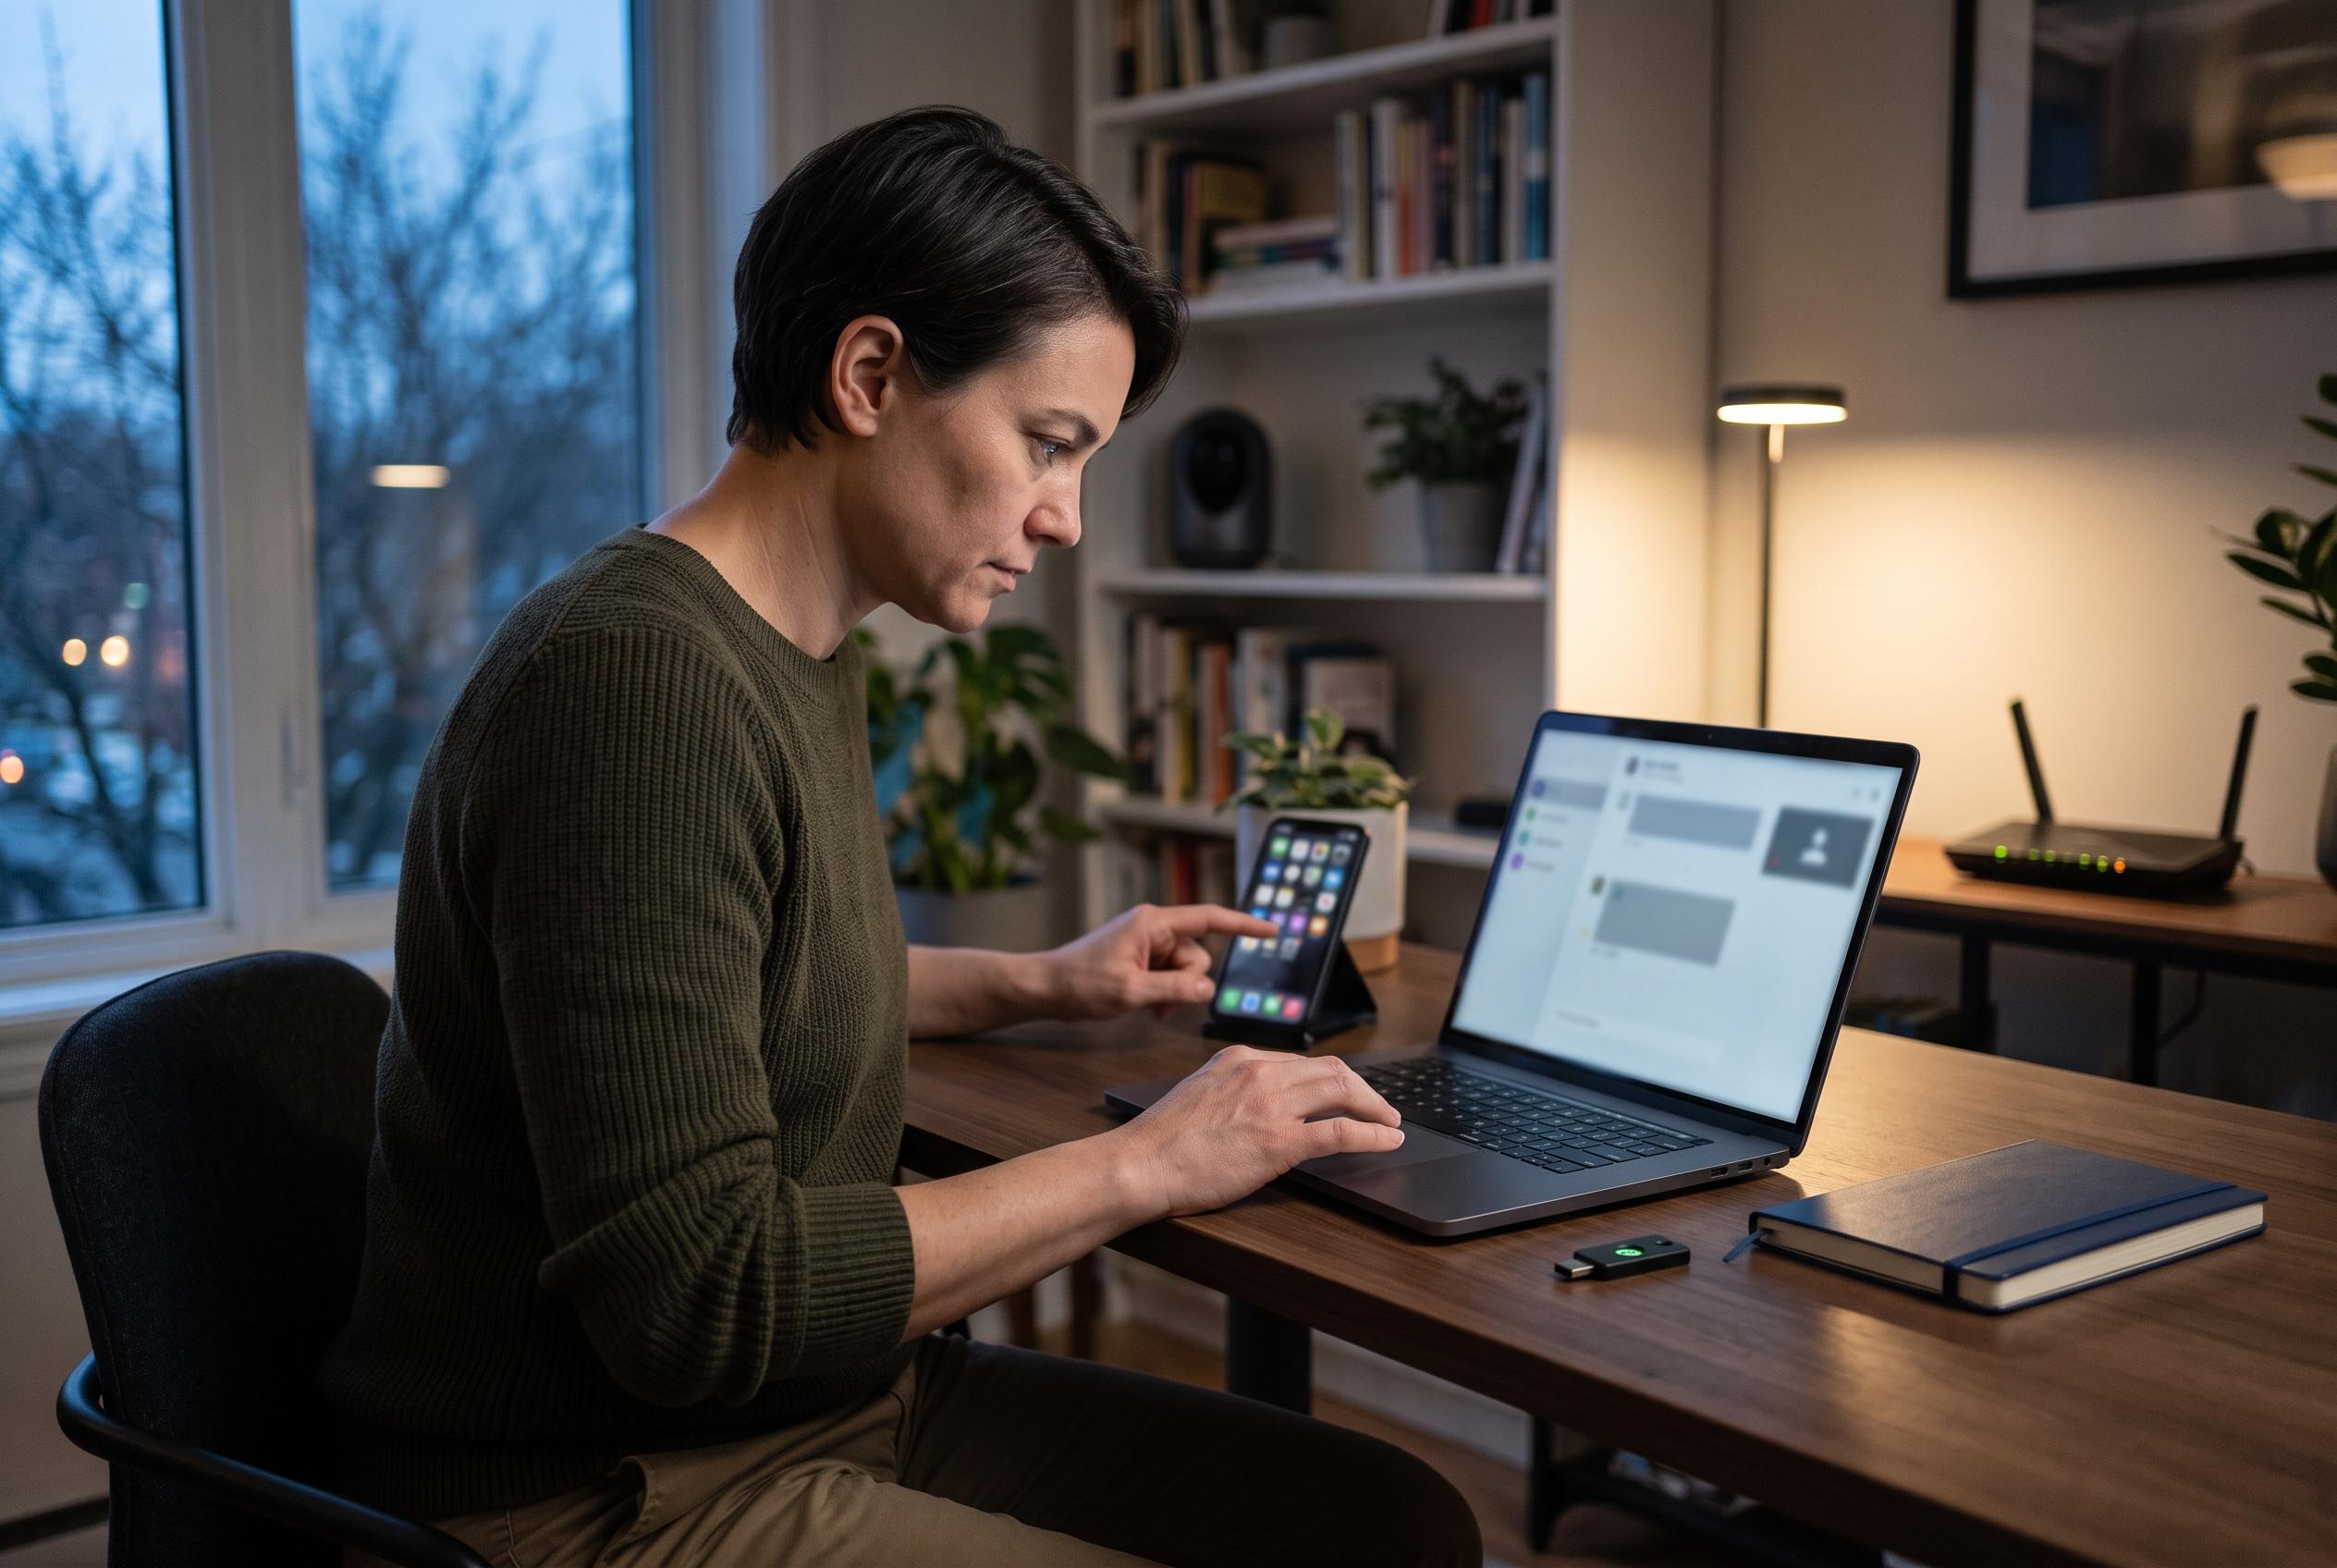

As more Americans incorporate chatbots into their daily routines, concerns over privacy and data protection intensify. Experts warn that users often underestimate how personal information shared with AI tools can be stored, used, or misused, prompting calls for stronger regulations and safer default settings.
More people are folding chatbots into daily routines, but the privacy risks remain substantial. Pew Research Center found in June 2026 that 44% of US adults had used ChatGPT, up from 34% a year earlier, while other tools such as Gemini, Copilot and Meta AI trail behind. Pew also found the strongest uptake among younger adults, underlining how quickly these systems are becoming normalised. Reuters has reported similar concerns from researchers and security specialists: the more conversational these tools feel, the easier it is to overlook how much personal material users may be handing over.
That caution matters because several major AI developers appear to use customer conversations to train and improve their systems by default, according to a Stanford Institute for Human-Centred Artificial Intelligence review of privacy policies. The study said some providers retain data indefinitely. Cybersecurity experts quoted by HuffPost warned that many users underestimate how prompts, files and follow-up exchanges can be stored, analysed and, in some cases, reused beyond the original session.
The most obvious category to keep out of a chatbot is personally identifiable information. That includes names, addresses, phone numbers and government identifiers such as passport or driving licence numbers. Experts said such details can create exposure to identity theft, phishing or data brokerage. Uploaded documents raise the stakes further, because resumes, forms and other files may contain hidden identifiers unless they are removed first.
People should also be wary of sharing intimate personal material, medical records, workplace secrets and financial documents. HuffPost cited privacy specialists and university guidance warning that chatbots are not the same as doctors, therapists, lawyers or confidential enterprise systems, and that a prompt can become a permanent data trail. That is especially important in regulated settings, where a single message containing client information, source code or banking details could breach contracts, internal policy or compliance rules.
If sensitive information has already been shared, experts say the next step is damage limitation rather than perfect erasure. Deleting chat history may reduce the risk of account compromise, but it does not guarantee removal from a model’s training data. The safer approach is to treat AI conversations as semi-public, use general descriptions or pseudonyms, and check privacy settings carefully. Stanford researchers have argued that better defaults, clearer opt-in rules and stronger privacy regulation are needed if AI is to expand without normalising routine data leakage.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.