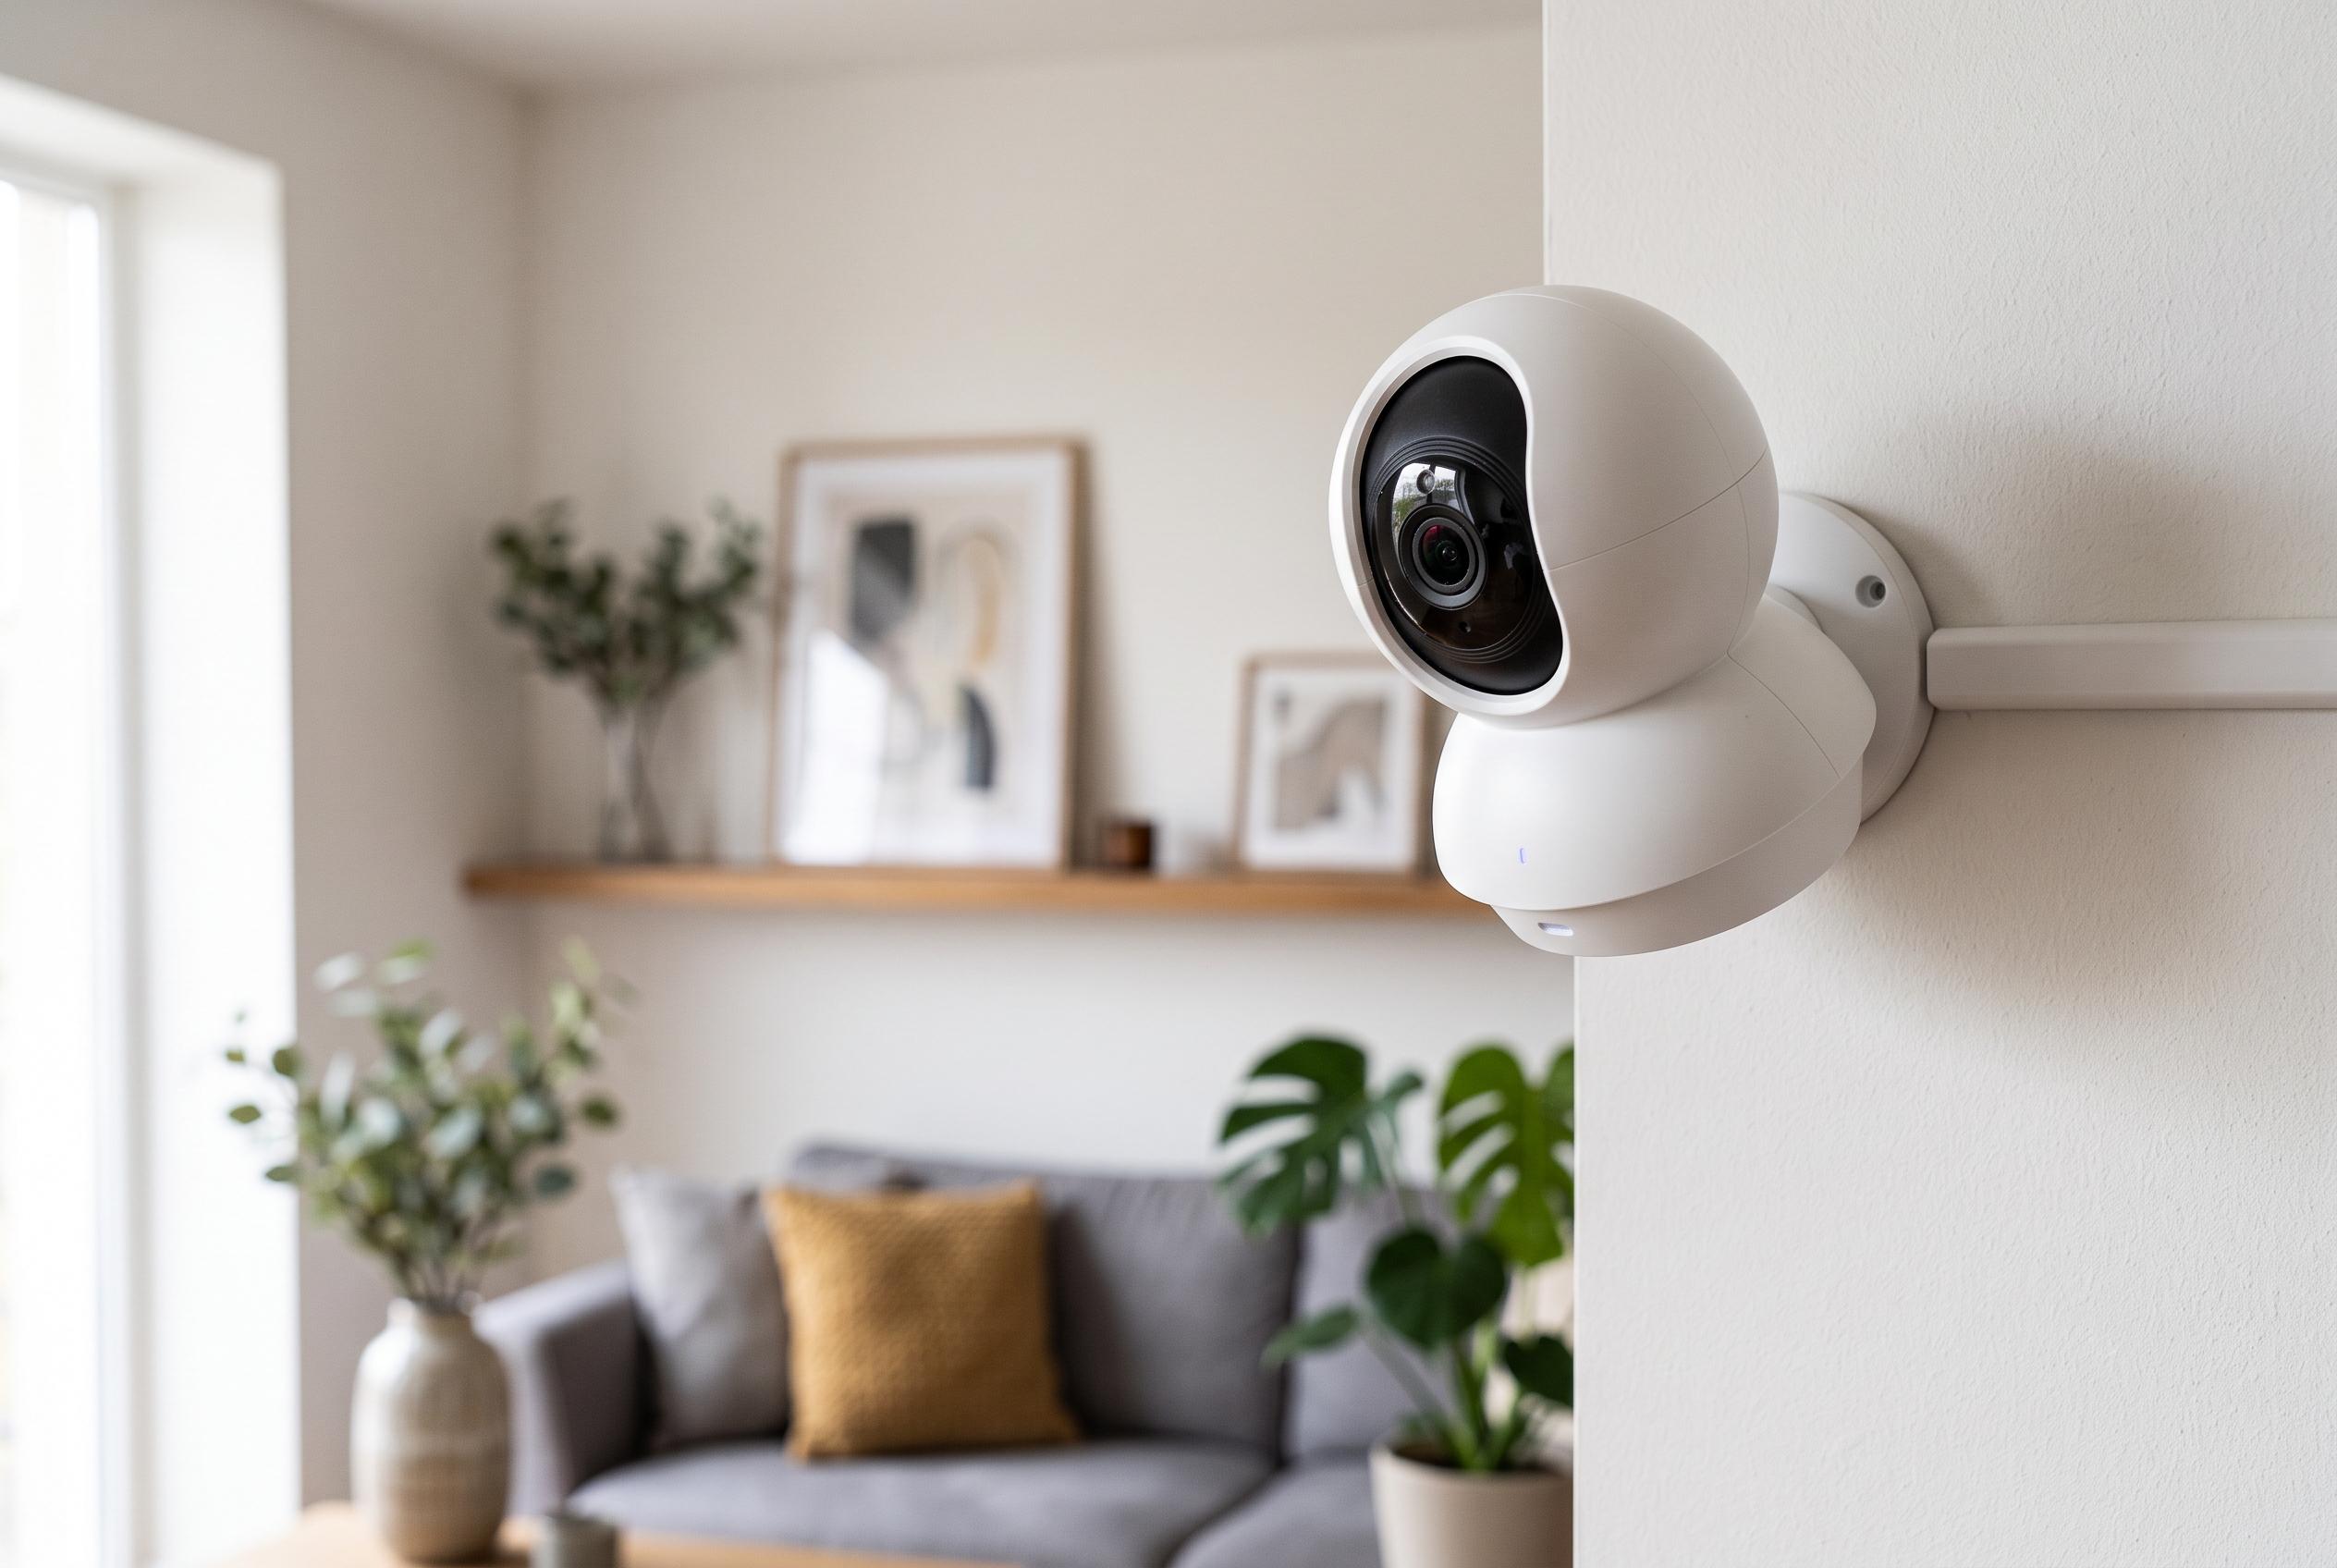

Owners of TP-Link Tapo C200 security cameras must update to the latest firmware following disclosures of two critical zero-day flaws that could allow hackers to take control and access private footage.
Owners of the TP-Link Tapo C200 should install the latest firmware without delay after researchers disclosed two zero-day flaws that could let an attacker take control of the device and watch its camera feeds. OPSWAT said the issues, tracked as CVE-2026-15315 and CVE-2026-15316, affect cameras exposed to the network and could be abused to obtain administrative access without recovering the password.
According to OPSWAT, successful exploitation would allow an intruder to use privileged management functions, alter settings and reach both live video and recorded footage. That raises obvious concerns for devices used as baby monitors or for general home security, where unauthorised access could expose some of the most private parts of a household.
TP-Link said it investigated the report after being notified and produced a firmware fix. The company’s US support page lists V5-1.4.6 Build 260709, released on 17 August 2026, as the latest version for the Tapo C200 v5 model, with release notes that include stability and security improvements, alongside performance tweaks for live streaming and SD card recording.
The company is urging customers to update through the Tapo app or by using the support pages for their specific hardware revision. That distinction matters because TP-Link maintains separate download pages for different versions of the same camera, and the available firmware can vary by region and model branch.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.