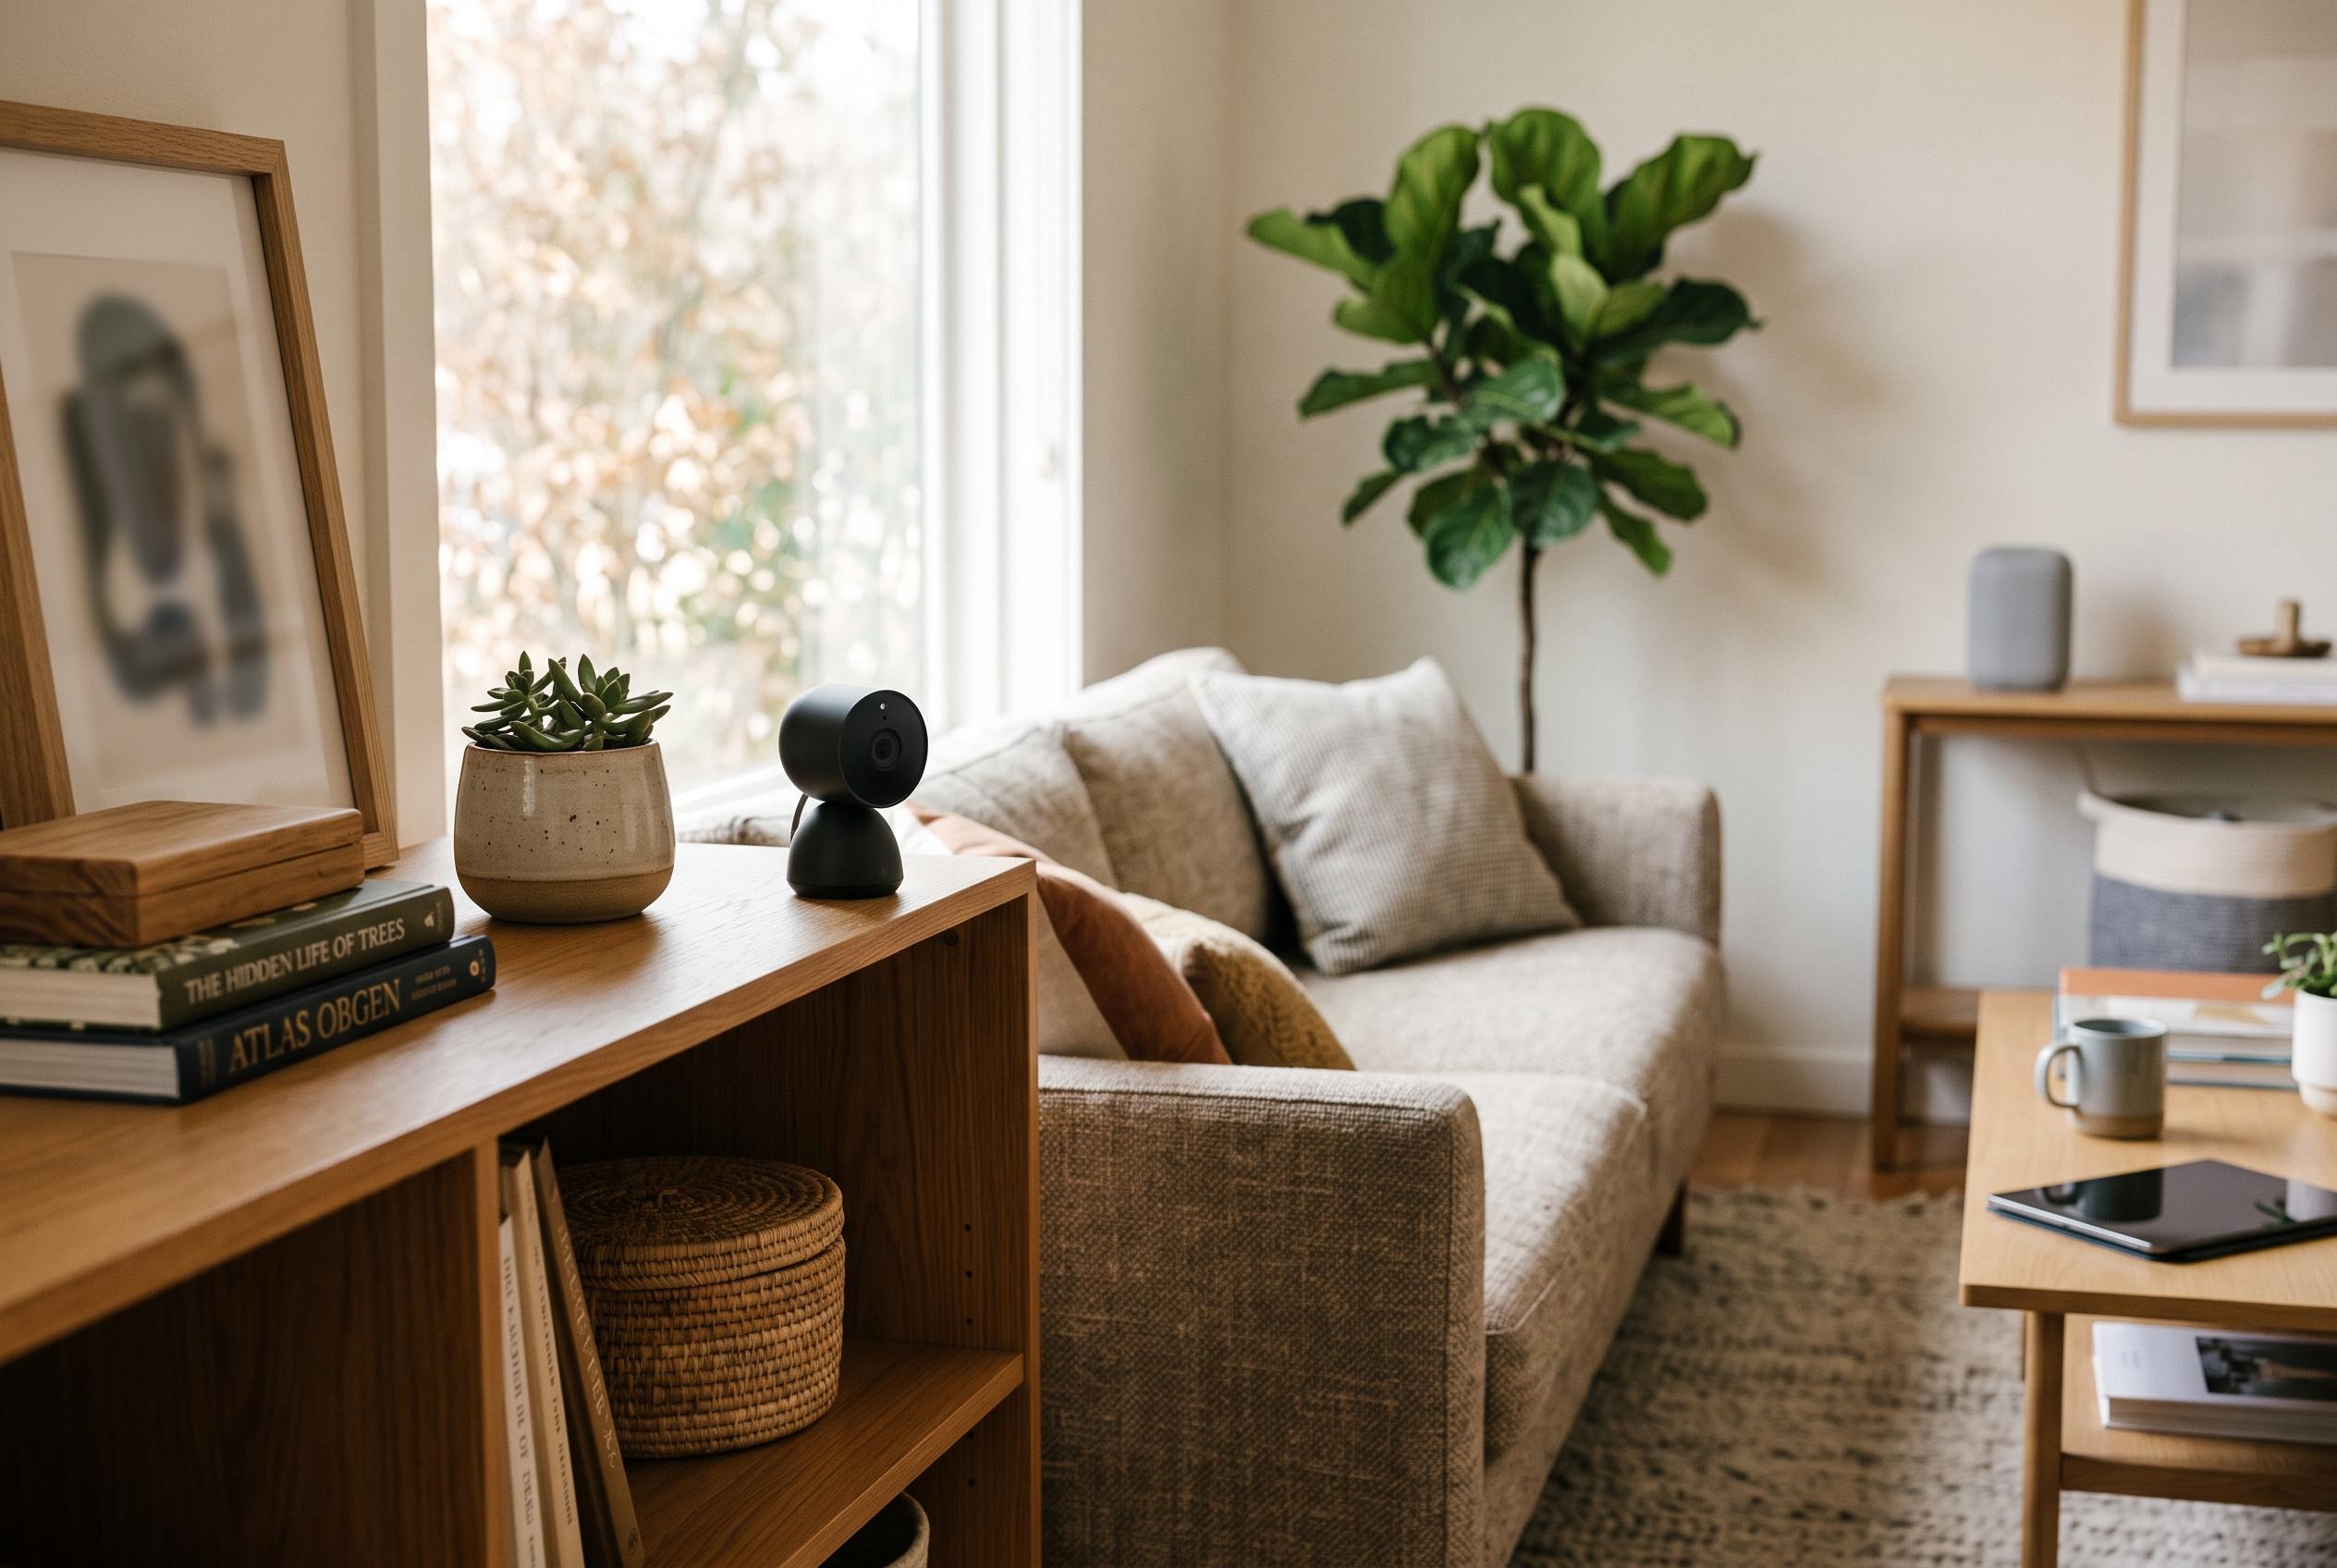

Owners of affected Tapo C120 and C200 cameras are urged to install updated firmware after researchers found flaws that could enable administrator-level control from the local network.
TP-Link users have been urged to install the latest firmware on Tapo security cameras after researchers showed that multiple flaws could let an attacker seize control of affected devices, alter settings and, in the worst case, use the camera as a foothold for wider attacks on a home network. According to TP-Link’s own security advisory, the affected models include the Tapo C120 and C200 families, and the company says fixes are now available.
The most serious issue, described as CVE-2026-102369, is a remote code execution flaw linked to a diagnostic service intended for manufacturing and maintenance. Researchers from OPSWAT’s Unit 515, Khoi Tran and Thai Do, said the weakness can be chained with an authentication bypass first disclosed in September. In practice, that combination can give an attacker administrator-level access without needing the owner’s password, provided the attacker is already on the same local network. SentinelOne’s entry on the flaw says the bug allows unauthenticated command execution inside the device management process.
The same research also identified three further weaknesses. One, tracked as CVE-2026-78578, allows unauthorised changes to wireless settings and can disconnect the camera from Wi-Fi, creating a denial-of-service condition. Another, CVE-2026-78577, can expose details of nearby wireless access points, including network identifiers that may reveal elements of the local wireless environment. A third issue, CVE-2026-9032, can stop the camera’s HTTPS service. SentinelOne separately notes that CVE-2026-78577 can disclose metadata about nearby access points, while CVE-2026-78578 can be used to alter wireless configuration without authentication.
Although the findings are serious, the attack path is not remote in the broad internet sense. The researchers said the exploit chain requires access to the same local network, which makes opportunistic abuse harder than a fully internet-facing flaw. Even so, security specialists quoted in the coverage say the practical risk is significant because a compromised camera could be used to probe other devices on the same network. TP-Link says the vulnerabilities have been patched in updated firmware, and users are being told to apply those updates immediately.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.