
Experts emphasise that isolating IoT devices on separate virtual networks significantly reduces the risk of widespread compromise, marking a pivotal shift in home and small-office cybersecurity strategies.
IoT convenience often comes with a hidden cost: a wider security perimeter. Smart thermostats, cameras, locks and similar devices are typically built for ease of use rather than rigorous defence, and that makes them attractive targets for attackers. Geeky Gadgets, drawing on NetworkChuck’s guidance, argues that the safest approach is to stop treating every connected device as part of one open domestic or office network. Instead, the aim should be to contain lower-trust devices so that a compromise in one corner does not automatically expose everything else.
That warning is consistent with the broader security guidance from firms such as Cloudflare, Fortinet and TechTarget. Their material notes that IoT devices are frequently weakened by default credentials, weak or hardcoded passwords, insecure interfaces, limited patching and outdated firmware. GeeksforGeeks adds that the problem is not just the weaknesses of individual devices, but the scale of connectivity itself: each new endpoint increases the attack surface and gives criminals more opportunities to probe, exploit and persist. Once a device is compromised, it can become a foothold for lateral movement, malware delivery or covert surveillance.
The most practical defence is network segmentation. In the home or small-office context, that usually means placing IoT equipment on a separate virtual network, often using Virtual Local Area Networks, or VLANs. A VLAN lets a single physical network be divided into isolated sections, so that connected devices behave as if they were on separate networks. The benefit is straightforward: if a camera or smart speaker is breached, the attacker should not be able to roam freely towards laptops, file servers or work systems. TechTarget’s enterprise guidance makes the same point in broader terms, stressing that segmentation reduces exposure and limits the damage caused by a single compromised endpoint.
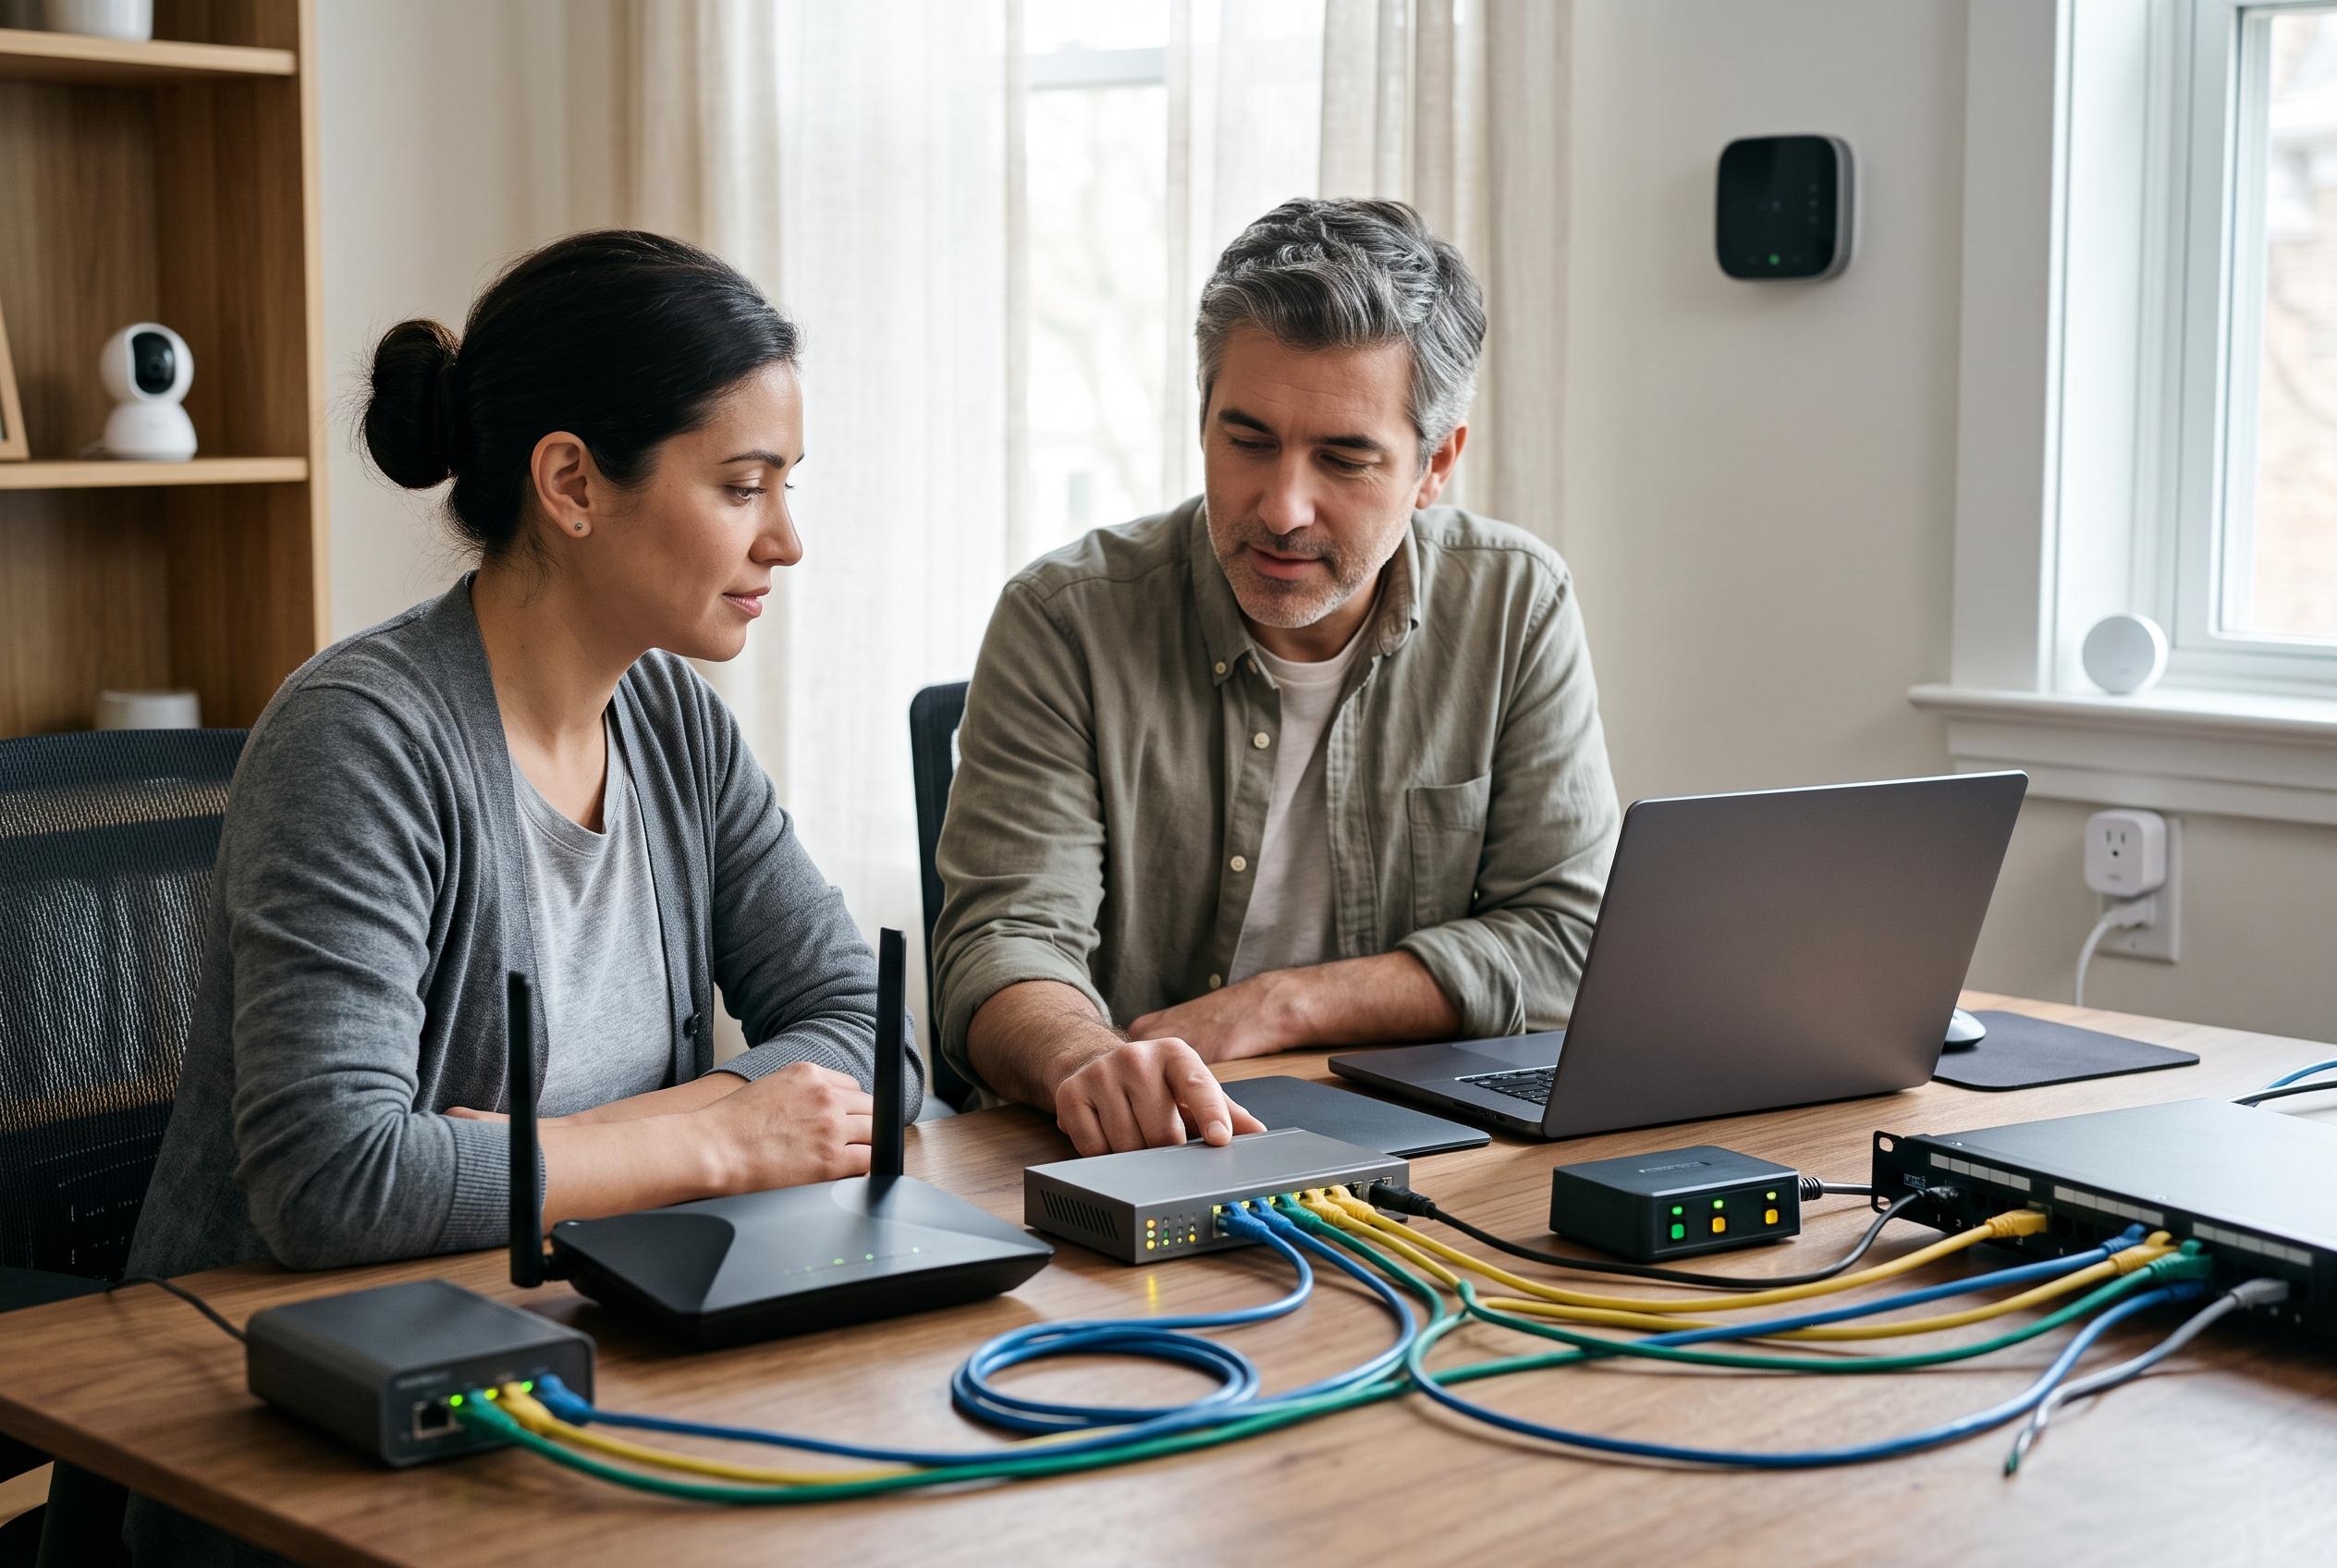
Setting that up requires more than simply naming a guest Wi‑Fi network. As Geeky Gadgets explains, a managed switch or VLAN-capable router is usually needed to create the separate segments, alongside correctly assigned DHCP ranges and firewall policies that define what may talk to what. The safest baseline is a default-deny posture, then allowing only specific traffic where there is a clear need, such as a phone controlling a thermostat. The same source also highlights the common errors that can undo the work: incorrect VLAN tagging, badly matched DHCP settings and firewall rules that either block legitimate traffic or leave gaps that should not exist.
There is also a case for layered protection beyond segmentation. Multiple Wi‑Fi SSIDs can help separate IoT gear from more sensitive devices, while regular firmware updates remain essential because many device makers patch vulnerabilities slowly, if at all. The article also points to AI-based monitoring as a useful addition, particularly where unusual traffic patterns or unauthorised connections need to be spotted early. That is not a replacement for segmentation; it is a second line of defence. In practice, the most resilient setup is the one that assumes devices may fail, then limits how far failure can spread. For readers building or revising a home network, that is the key lesson: convenience should not come at the price of leaving every device on one open trust zone.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.