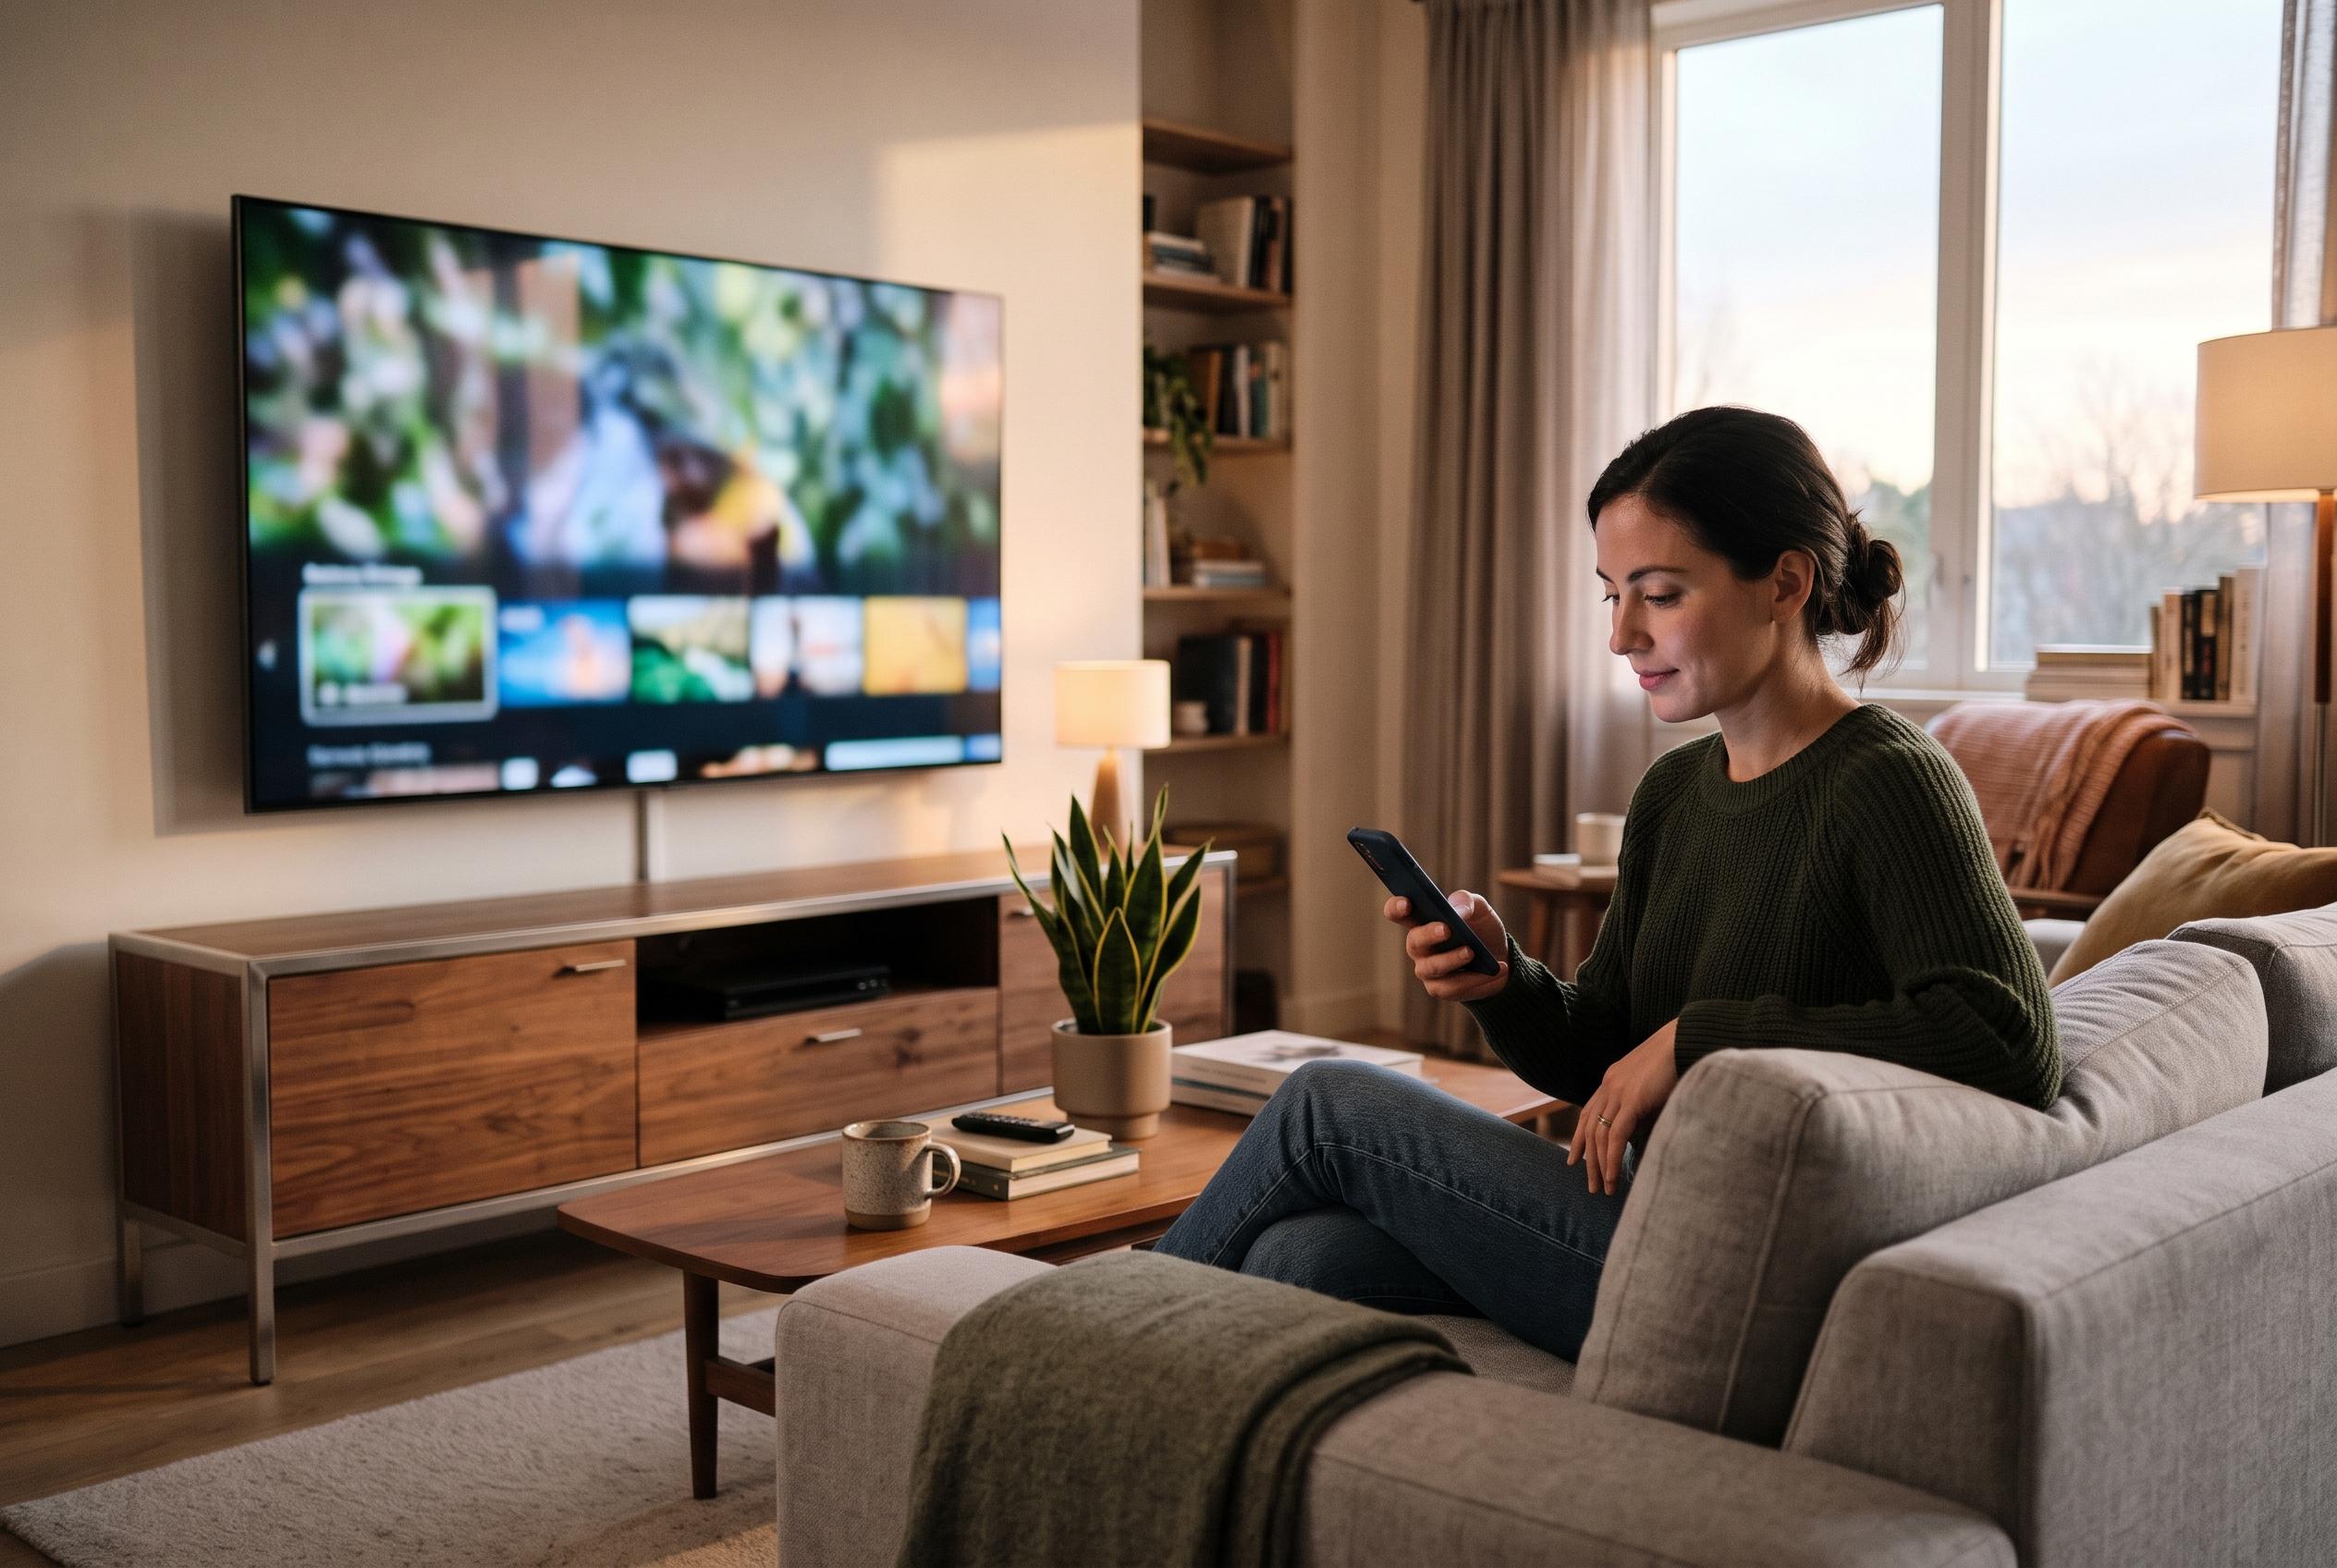

A researcher claims code in a 2025 Samsung television points to extensive viewing telemetry, audio analysis, screenshots and cross-device tracking, though independent testing remains limited.
A cybersecurity researcher posting under the handle log4j has claimed that a 2025 Samsung television was transmitting far more user data than many owners would expect, after the set appeared to deliver unusually specific advertising. According to Tom’s Hardware, the researcher then reverse-engineered the Tizen operating system and said they found code linked to detailed telemetry, audio categorisation, screenshots and cross-device identification designed to improve ad targeting.
The most troubling part of the discovery, as described by Tom’s Hardware and a related summary of the findings, was the breadth of the data collection routines. The researcher said the television appeared to process viewing behaviour on the device itself, including which videos were watched, which advertisements were skipped and how far playback had progressed. They also reported evidence of software that could look for microphones on connected equipment, such as a soundbar or Bluetooth device, if the television itself lacked one. In the reporting, the researcher theorised that this processing could also help explain why some smart TVs feel sluggish, although that remains an inference rather than a proven cause.
A separate observation from Hugging Face engineer ngxson added a limited data point, after they used a Flipper Zero to test the microphone behaviour and saw the television open the microphone for five seconds before stopping. They cautioned that their set had already been rooted and had some settings disabled, so the result may not reflect how an untouched retail unit behaves. That distinction matters, because the test does not by itself establish what a stock television would do in the same circumstances.
The episode has also drawn attention because log4j said OpenAI later banned their account for cyber abuse after they used its tools during local reverse engineering. According to the researcher, they were not exploiting the television or searching for a live vulnerability, but were using the tools to help analyse firmware behaviour. Tom’s Hardware reported that the researcher disputed the ban and suggested an automated classifier may have triggered it. The case lands in a broader debate over smart-TV privacy, after other reporting and recent academic work have raised similar concerns about automatic content recognition, opt-out settings and continued tracking traffic from connected televisions made by major brands.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.