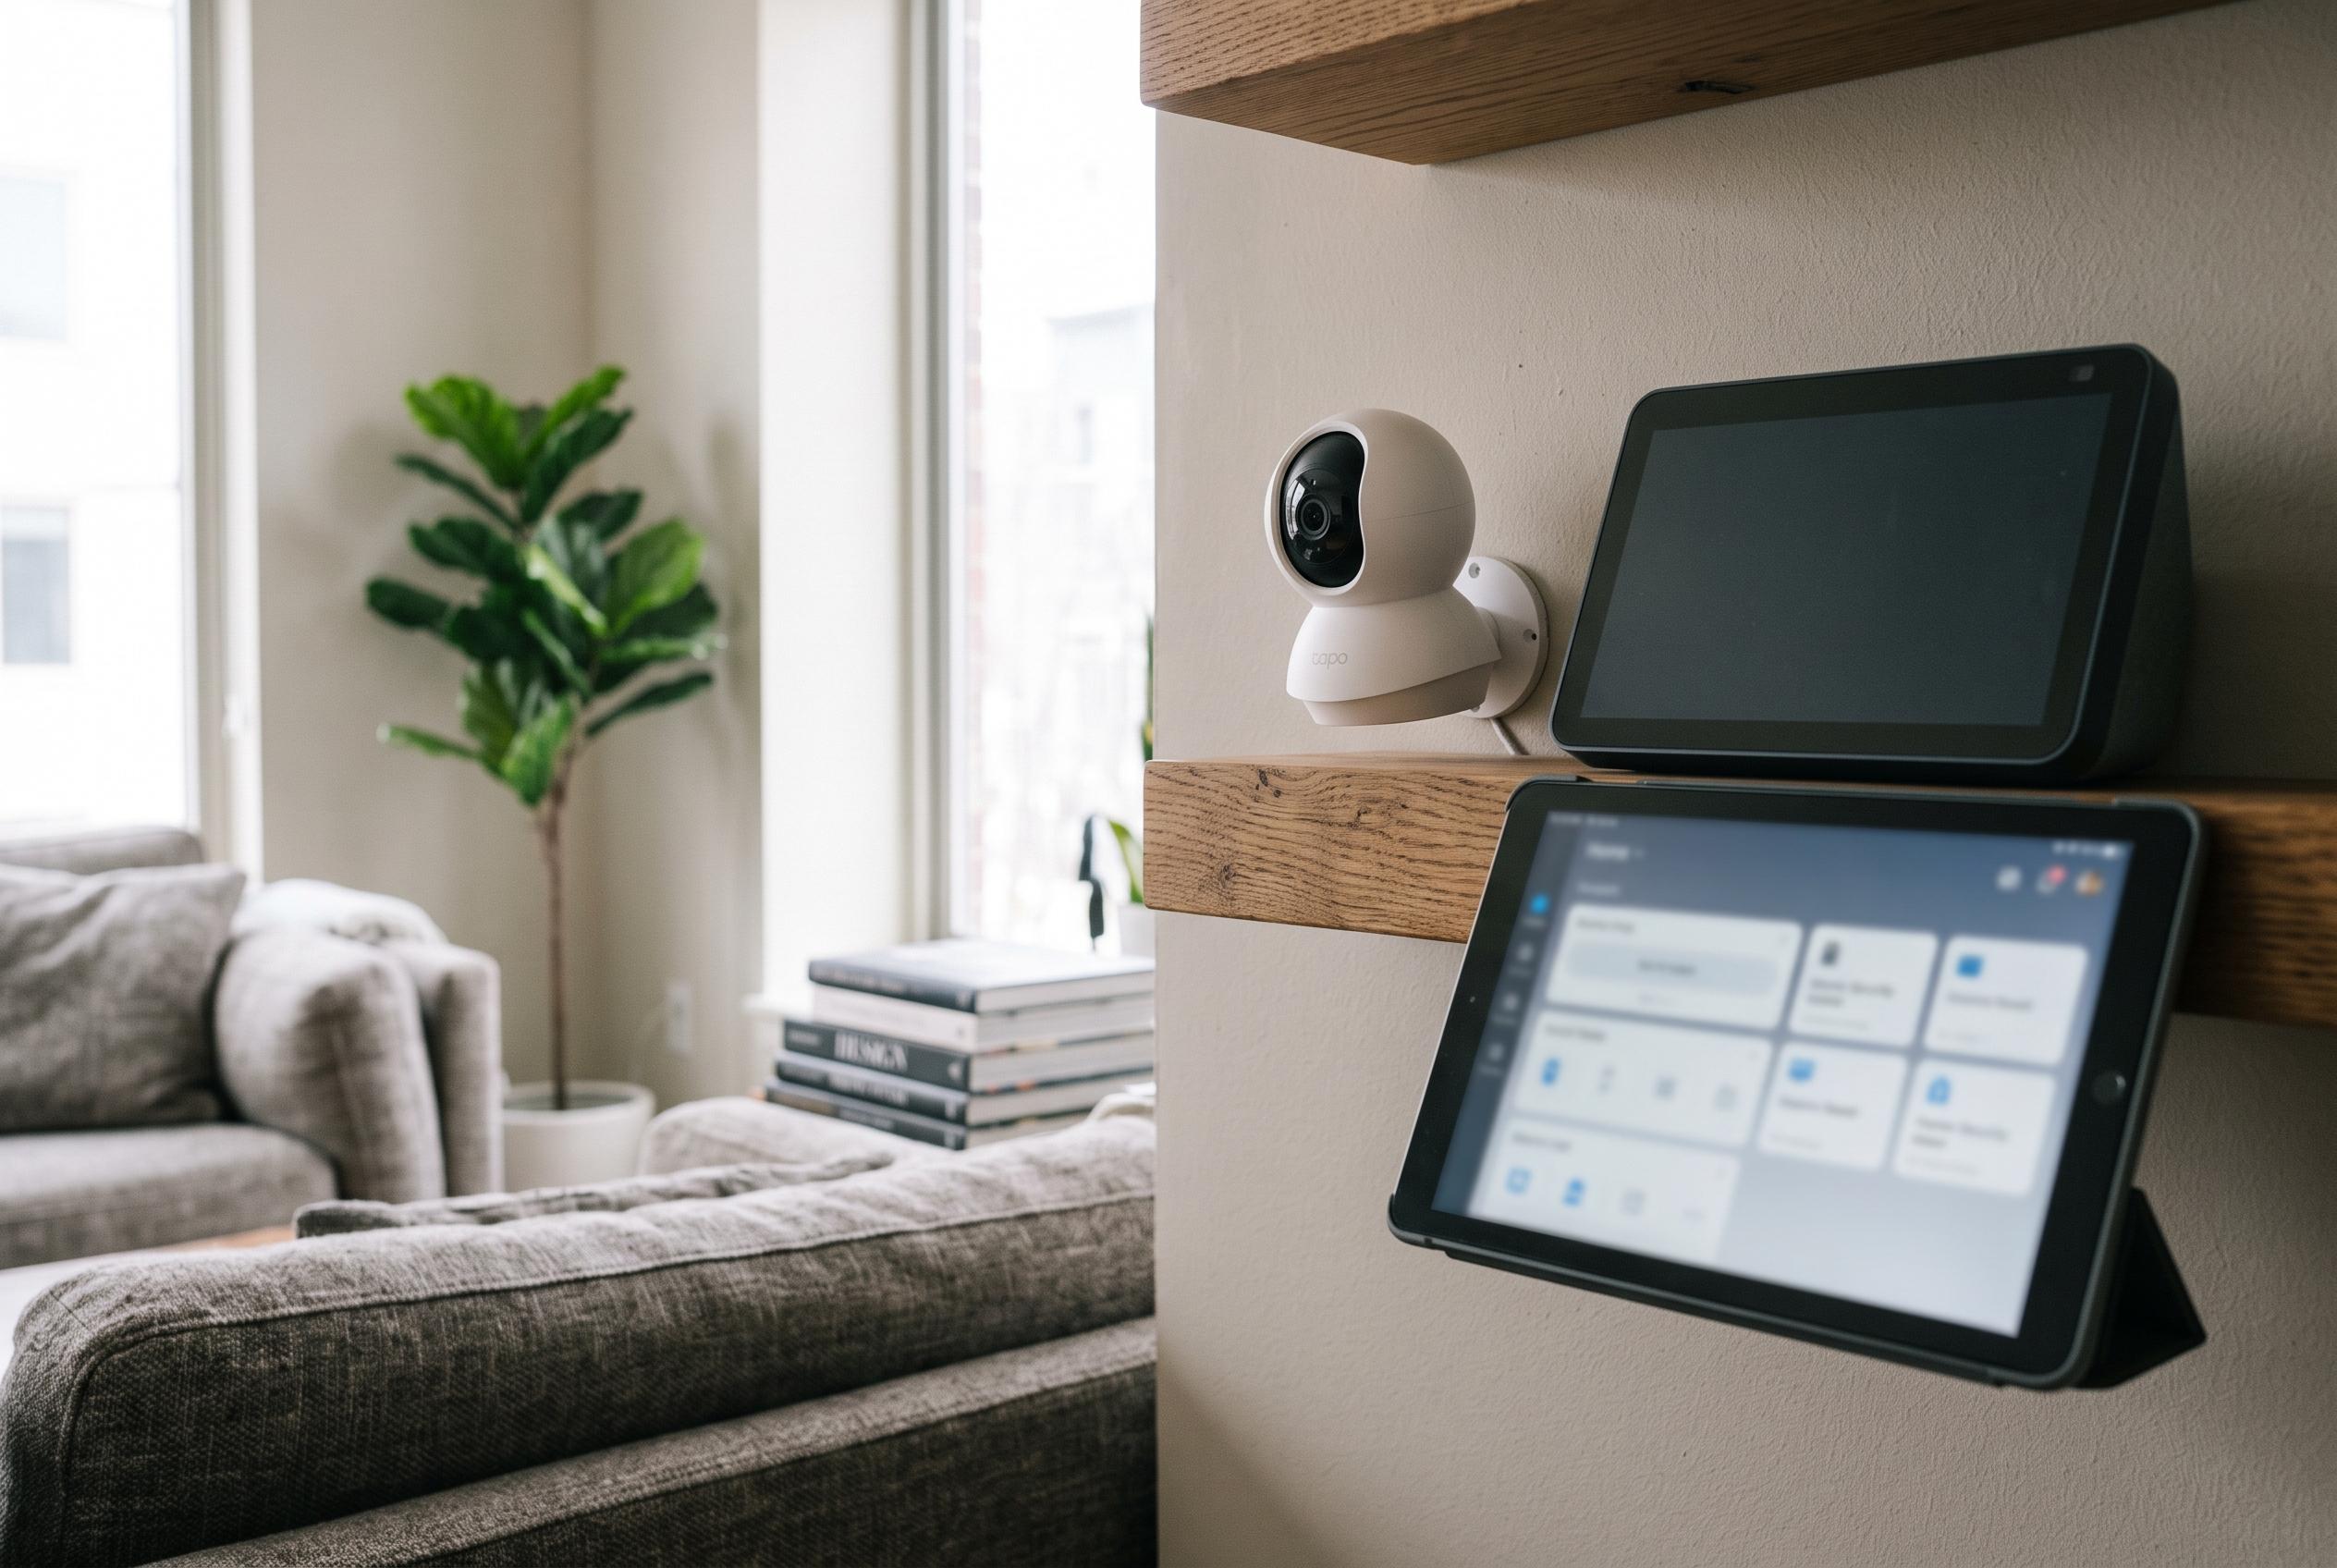

TP-Link has released a security update for its Tapo C200 v5 home camera following the discovery of flaws that could allow attackers to control the device or cause it to go offline, impacting models Tapo C120 v1 and Tapo C200 v5.
TP-Link has issued a security update for its Tapo C200 v5 home camera after researchers found flaws that could let an attacker take over the device or knock it offline. According to TP-Link’s advisory, the problems affect the Tapo C120 v1 and Tapo C200 v5 models and are tracked as CVE-2026-15315 and CVE-2026-15316. The first carries a CVSS score of 8.7 and is described as an authentication bypass that can expose administrative access; the second scores 7.1 and can trigger a denial of service through malformed encrypted input.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.