
Network-attached storage devices are increasingly powerful , and increasingly attractive to attackers. Experts urge households to close unnecessary internet access, limit permissions and keep independent backups.
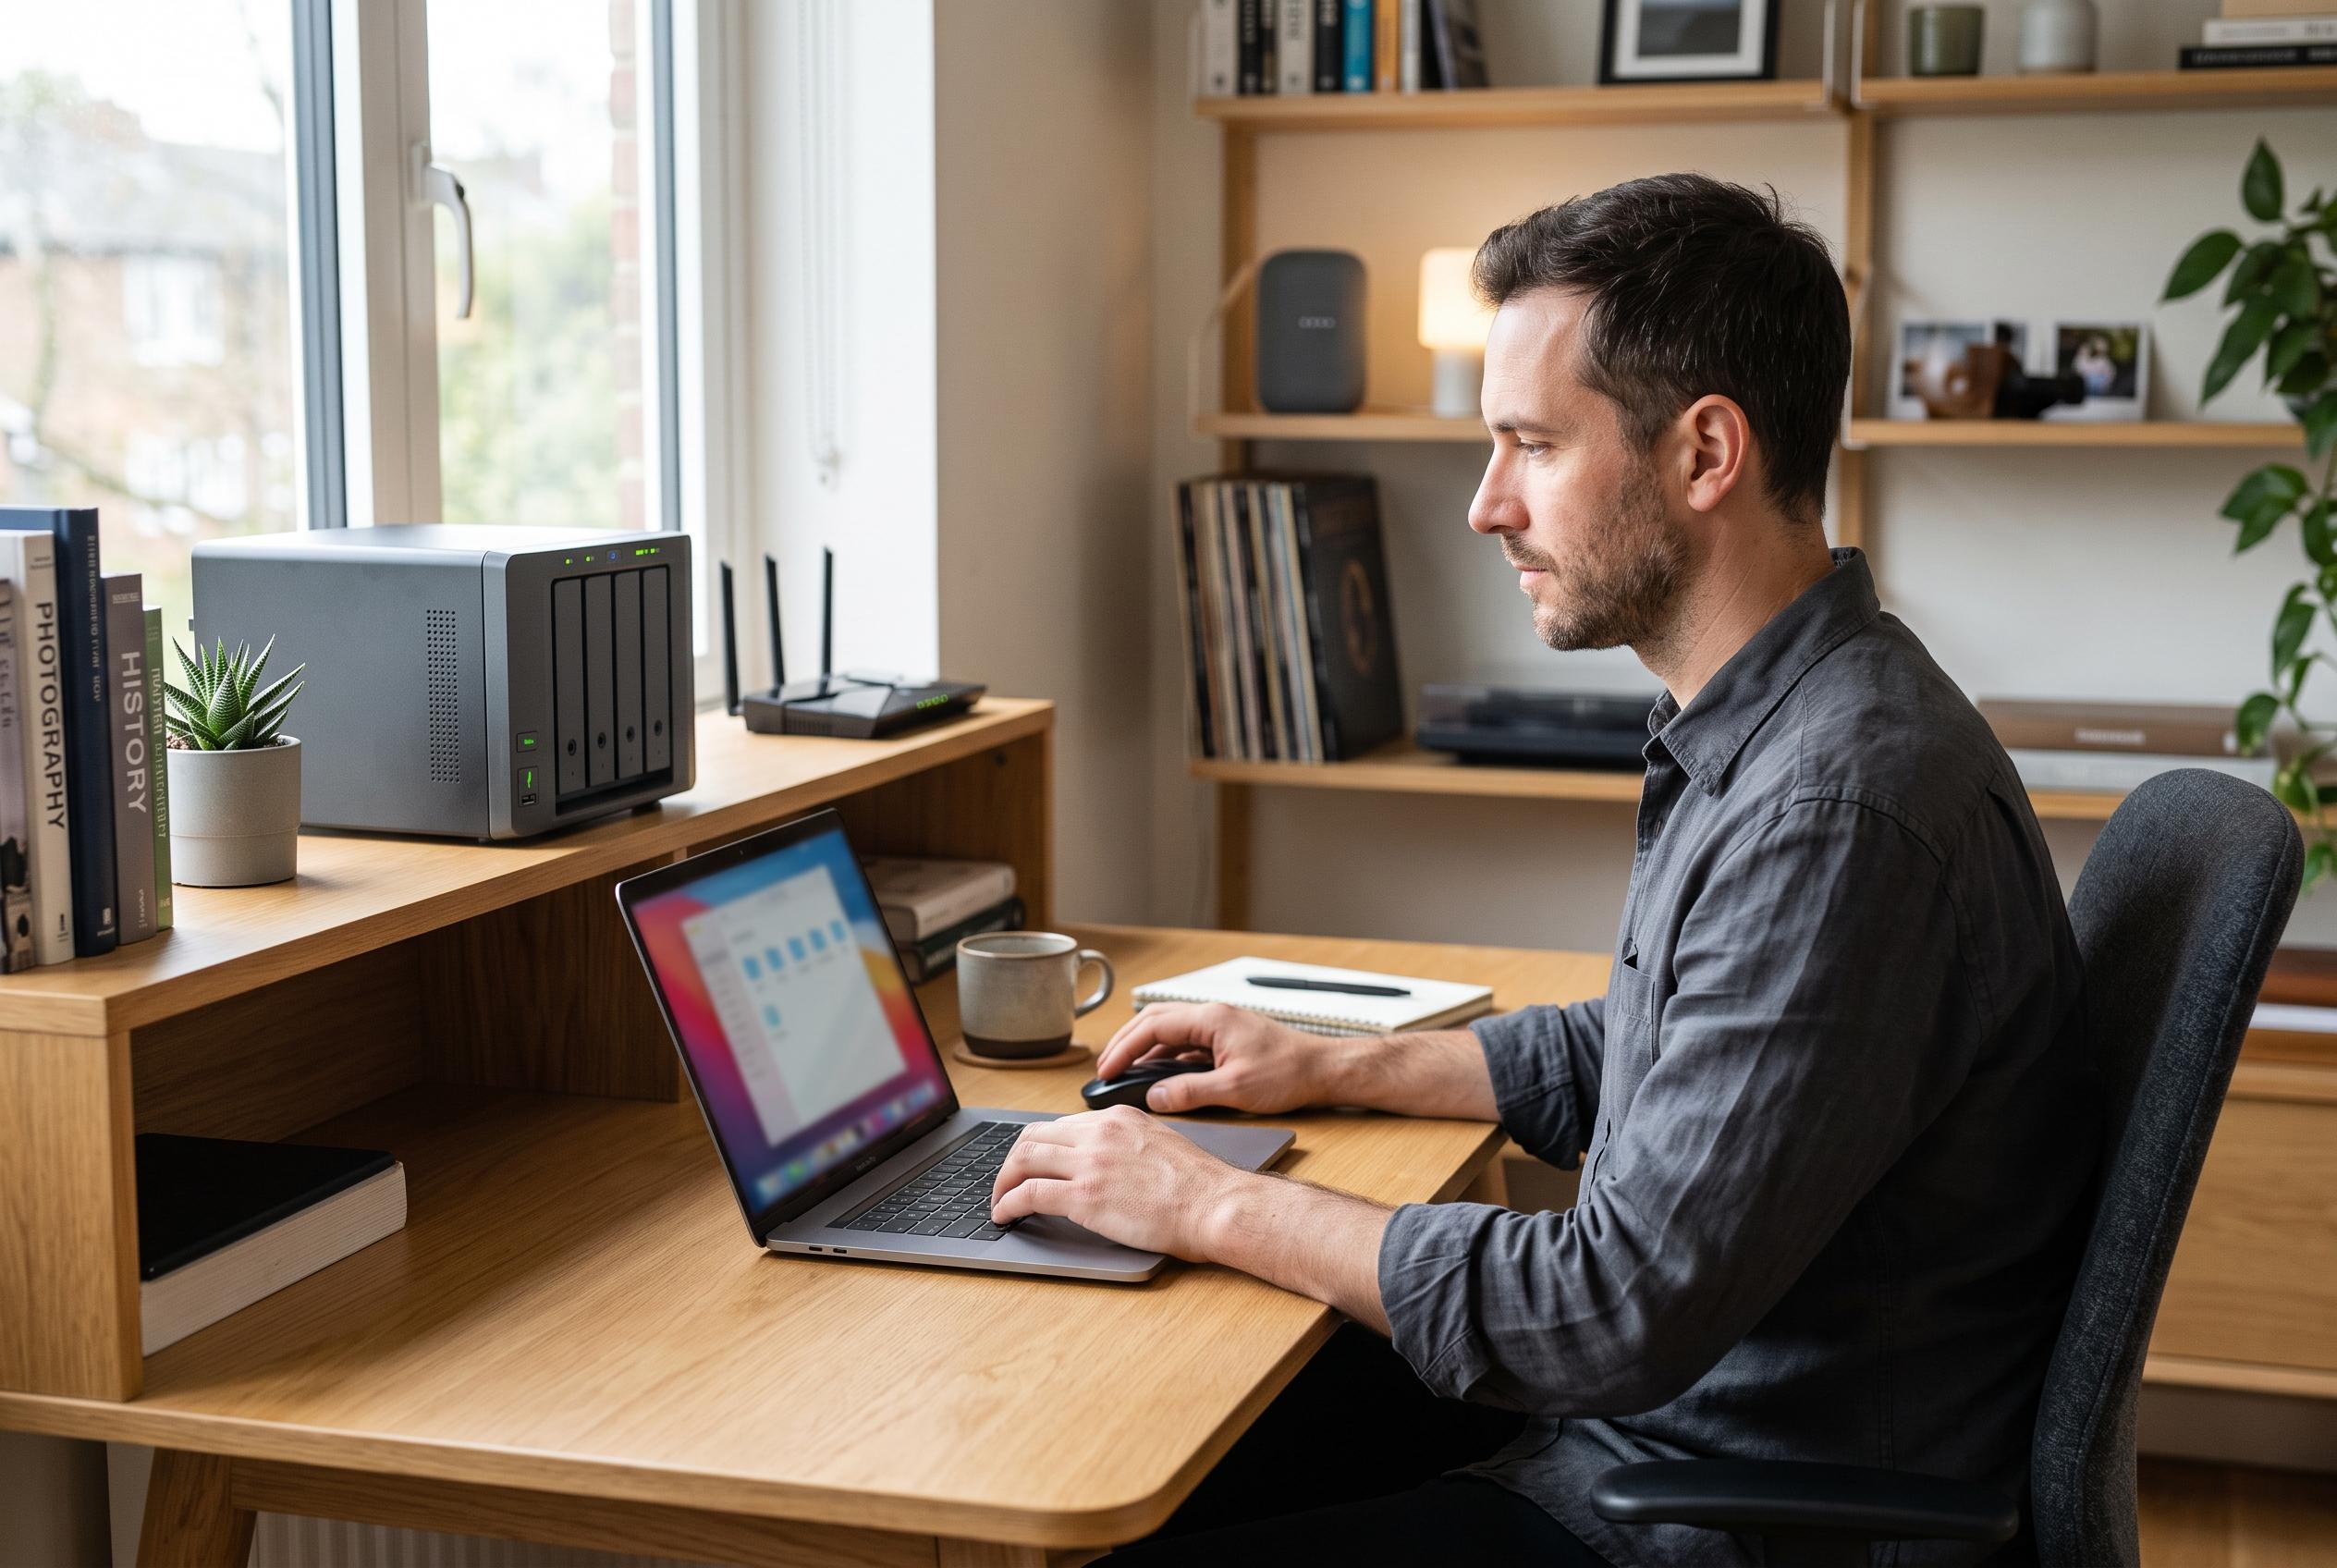
A network-attached storage device can be one of the most useful pieces of kit in a home, but it should never be treated as a passive hard drive. According to TechBusiness News, modern NAS units now behave much more like small servers, with operating systems, remote-access tools, file-sharing services, applications and, in some cases, virtual machines. That extra capability is also what makes them attractive to attackers when they are left poorly secured. Recent vendor advisories underline the point: Synology’s September 2026 security bulletin described multiple DSM vulnerabilities with high severity ratings, while QNAP continued issuing warnings in 2026 about flaws affecting a wide range of its systems.
The core mistake many households make is to assume that a NAS is harmless because it sits behind a router. In practice, it often becomes one of the most trusted devices on the local network, holding photographs, backups, documents and media libraries in one place. As TechBusiness News noted, that makes it a valuable target if an attacker reaches it through a weak password, an exposed service or an unpatched application. CISA has repeatedly warned that internet-facing systems with default settings or outdated software can be probed automatically, without any specific targeting of the household.
A safer way to think about a NAS is as a computer that happens to store files. It may run SMB file shares, browser-based administration, cloud synchronisation tools, backup jobs, media servers, surveillance software, containers and database services. Each function expands the attack surface. The more services a device runs, the more opportunities there are for an attacker to find a weak point, so unused features should be turned off rather than left available by default.
The biggest risk rises sharply once a NAS is exposed directly to the internet. Many users do this by forwarding router ports so they can reach files from outside the home. That may appear convenient, but it can turn the NAS into an internet-facing server that is continuously visible to automated scanners. CISA advises removing unnecessary internet exposure and using stronger remote-access controls where access is genuinely required.
File-sharing protocols deserve particular caution. CISA specifically warns against exposing SMB, the protocol commonly used by Windows computers to reach NAS shares, directly to the public internet and recommends blocking external traffic on TCP port 445. For most homes, there is little reason to publish SMB at all. If remote file access is needed, a VPN or another authenticated access layer is far safer than opening the share itself.
The same logic applies to FTP and SSH. These tools are useful for some administration tasks, but CISA says they should not be exposed unless they are genuinely necessary. Traditional FTP can be insecure if not properly protected, while SSH, although encrypted, still becomes a point of attack once it is reachable from outside the network. QNAP has also advised users to disable unnecessary services and avoid direct exposure of NAS devices to the internet.
Network segmentation can reduce the damage if something does go wrong. Rather than placing the NAS on the same flat network as every other device, a better design is to isolate it on a separate VLAN and allow access only from approved machines and services. CISA says segmentation helps limit lateral movement, which is the stage of an intrusion where an attacker tries to move from one device to another after gaining a foothold. In a home setting, that may mean allowing one PC to back up to the NAS while blocking smart televisions, cameras, guest Wi-Fi devices and miscellaneous internet-connected gadgets from reaching it.
Ransomware makes the case for stronger protection even more urgent. A NAS often stores the very backups people expect to rescue them after an infection. But if a compromised computer has write access to the shares, ransomware can encrypt the backup copy as well as the original files. If the NAS itself is compromised, the attacker may be able to delete, encrypt or steal the stored data directly. That is why a NAS should be part of a broader backup plan rather than the only backup.
Snapshots can help, but they are not a complete defence. They can provide a fast way to roll back accidental deletions and some ransomware damage, yet a sufficiently privileged attacker may still be able to remove them. A more resilient arrangement keeps at least one additional backup copy on independent external or off-site storage. That approach reduces the chance that a single compromised account or machine can destroy every copy at once.
RAID is often misunderstood in the same way. It improves availability if a drive fails, but it does not stop hacking, ransomware or accidental deletion. If malicious software encrypts a file on a RAID array, the encrypted version is what gets stored. If an administrator deletes a folder, RAID faithfully preserves the deletion across the set of disks. In security terms, RAID is a resilience feature for hardware failure, not a substitute for backup or access control.
Administrator accounts also need special care because they control the whole system. They should use unique, long passwords and multi-factor authentication wherever the NAS supports it. Ordinary family members and applications should use limited accounts instead of the master login, and permissions should be granted only where they are needed. A media player does not need access to tax records; a camera should only be able to write to its own folder; and a backup task should not automatically inherit full control over everything else.
This matters even more on modern NAS devices that support Docker containers and virtual machines. Those features can be extremely useful, but they add more software layers that must be maintained. QNAP’s 2026 guidance on container security urged users to trust only verified images and avoid privileged container operation unless absolutely necessary. A vulnerable or over-permissioned container can become another route into the broader system.
The practical conclusion is straightforward. Keep the NAS operating system and installed applications updated, review port forwarding and UPnP settings, disable services that are not needed, avoid exposing management pages or SMB directly to the internet, and segment the device away from general household traffic where possible. A NAS can be one of the most valuable devices in a home, but only if it is treated as a server with a security boundary, not as a simple storage box.
Disclaimer: This content is intended for informational purposes only. Readers are advised to exercise their own judgement, conduct due diligence, or consult a qualified expert before acting on any information provided.